FedRAMP certification now runs through FedRAMP 20x, and the Consolidated Rules for 2026 become mandatory for every cloud service provider on January 1, 2027. If you sell software to federal agencies, that date is the one to put on the wall. However, the rules took effect in early July 2026. The Class A, B, and C application pipelines are all open. FedRAMP stops accepting new Rev5 applications on June 11, 2027.
This guide explains what FedRAMP certification needs in 2026, what it costs, and how long it takes. It also shows whether the federal cloud market is big enough to pay for it. I have written it for the small software company, not the hyperscaler. Too many capable vendors lose a year to a certification path nobody explains to them. However, the 2026 rules change that path in ways that help a small vendor more than they help a large one.
By Jacob Grass, Founder, Procura Federal. Published November 9, 2026. Last updated November 9, 2026.
What is FedRAMP certification, and what changed in 2026?
FedRAMP is the federal program that reviews the security of cloud services before agencies buy them. The General Services Administration runs it. The core idea is reuse. GSA calls FedRAMP a “do once, use many times” framework, so one certification can support many agency authorizations.
Then, in 2026, two things changed. First, FedRAMP replaced its old document-heavy process with FedRAMP 20x, which uses machine-readable evidence and automated checks. Second, FedRAMP published the Consolidated Rules for 2026, a single ruleset that replaced a scatter of templates and memos.
The program also dropped a term many vendors relied on. FedRAMP now states plainly that it “does not support or provide” equivalency. For example, some sales teams tell agencies that a different audit makes them FedRAMP equivalent. As a result, that claim no longer has a home in the program.
In addition, one more change matters for the language you use. Specifically, FedRAMP moved from “authorization” to “certification” in its 2026 rules, and the Marketplace now lists classes in place of impact levels.
Who is required to be FedRAMP compliant?
In short, agencies, not vendors, decide this. The rules quote OMB Memorandum M-24-15: “Agencies are solely responsible for determining if their use of a cloud service falls within the scope of FedRAMP.”
The rules also list uses that fall outside FedRAMP. These exclusions are short and worth reading closely:
- Information systems that are only used for a single agency’s operations
- Social media and communications platforms used under agency social media policies
- Search engines
- Widely available services that provide commercially available information to agencies
- Ancillary services whose compromise would pose a negligible risk
However, here is the trap that catches small vendors. FedRAMP certification requires a government-wide use case. To get listed in the Marketplace and certified, a service must have direct government-wide use (used by multiple federal agency customers) or indirect government-wide use (used inside other cloud services that have direct government-wide use).
So read that again if you sell to one agency. In other words, a single-agency tool is excluded from FedRAMP scope, and it cannot get certified. That is not a gap in your paperwork. It is a structural answer, and it means the agency authorizes your service on its own terms instead. Know which side of that line you are on before you spend a dollar.
What are the FedRAMP 20x certification classes?
FedRAMP 20x uses four classes, A through D. A class describes how much assurance you give agencies, not how secure your service is. FedRAMP is explicit that the classes are presumptions and that agencies still categorize their own systems first.
| Class | Presumed adequate for | Status | Independent assessment | Automated checks per KSI |
|---|---|---|---|---|
| A | Pilots, configuration and testing, negligible-risk use | Open since Aug 3, 2026 | Optional | Optional |
| B | Most Low impact agency systems | Open since Aug 31, 2026 | Required, within 3 months | At least 1 (recommended, not mandatory) |
| C | Most Low or Moderate impact agency systems | Open since Aug 31, 2026 | Required, within 3 months | At least 2 |
| D | Most agency systems at any impact level | 20x path coming in 2027 | Required, within 3 months | At least 4 |
Also, Class B and C can support some High impact systems with compensating controls, per the rules. In contrast, Class D is the path for High impact work. FedRAMP lists the 20x Class D path as coming in 2027. Rev5 Class D remains available through the Agency certification path today.
Which FedRAMP certification class fits a small vendor?
Class A is the one small vendors miss. It is a Program path, so you need no agency sponsor. It also accepts an on-ramp many software companies already have. Class A requires a recent certification or equivalent (within 12 months) from FedRAMP Rev5, including the retired FedRAMP Ready, or SOC 2 Type II, or GovRAMP. As of November 2026, Class A carries 24 mandatory rules, 10 recommended, and 9 optional.
For example, if you hold a current SOC 2 Type II, you have a starting position in FedRAMP that did not exist two years ago. That is the single most useful fact in this guide for a small software company.
How do you get FedRAMP certified in 2026?
The sequence under the 2026 rules is short to describe and long to do:
- Confirm that you have a direct or indirect government-wide use case
- Get listed in the FedRAMP Marketplace, which comes before certification
- Choose a type (20x or Rev5), a path (Program or Agency), and a class
- Apply the FedRAMP Practices that match your target Certification Profile
- Build the Certification Package with implementation and validation evidence for each rule
- Engage a FedRAMP Recognized assessor if you target Class B, C, or D
- Apply directly, with a package verified within the previous 7 days
Next, a few mechanical rules catch vendors. You must apply directly, because FedRAMP does not accept third-party applicants. Your machine-readable data must validate against FedRAMP JSON schemas, and public JSON must be reachable by web applications with correct CORS headers. You cannot seek a Rev5 Program and a 20x Program certification for the same offering. Holding a Rev5 Agency certification alongside a 20x Program certification is allowed, but FedRAMP discourages it. You remain accountable for package accuracy even when consultants do the work.
Also, changing class later is not an edit. Upgrades and downgrades each require a new certification application. A downgrade wants at least 120 days of notice.
What are the Key Security Indicators?
Key Security Indicators, or KSIs, are the measurable security statements that replaced long control narratives. Class A names seven KSI rules as mandatory, alongside a security decision record rule: KSI-CMT-LMC, KSI-CNA-RNT, KSI-CED-RAT, KSI-IAM-AAM, KSI-IAM-APM, KSI-INR-RIR, and KSI-SVC-SIN.
In turn, the class you pick sets how much of the proof must be automated. FedRAMP recommends at least one automated method per KSI for Class B, without requiring it. Class C requires at least two. Class D requires at least four. FedRAMP also tells providers to apply all KSIs to every in-scope part of the offering, not only the parts a given class names.
In other words, this is the real engineering change in 20x. The old process rewarded a good technical writer. The new one rewards a system that can prove its own state on demand.
How much does FedRAMP certification cost?
FedRAMP does not publish a price. The best primary-source numbers come from GAO, which surveyed cloud service providers directly.
Specifically, in GAO-24-106591, eight of 13 providers reported what they spent pursuing authorization. The total was about $12.4 million, and the per-provider range ran from $300,000 to $3.7 million. One provider reported about $367,000. That figure included only its third-party assessment.
However, read that $12.4 million as a floor, not a total. GAO noted that four of the eight providers left out their labor and contractor support costs. The real spend was higher than the reported spend.
Also, those are Rev5-era numbers from a January 2024 report. FedRAMP has not published comparable 20x figures, and the honest answer is that 20x costs are still settling. Costs can fall for small vendors, because automated evidence replaces months of document work. But no .gov source yet measures that fall.
| Cost component | Range | Source type |
|---|---|---|
| Full authorization, per provider | $300,000 to $3.7 million | GAO survey (primary) |
| Third-party assessment only | About $367,000 | GAO survey, single provider (primary) |
| Readiness or gap assessment | $30,000 to $150,000 | Third-party estimate, directional |
| Annual continuous monitoring | $50,000 to $200,000 | Third-party estimate, directional |
How long does it take to become FedRAMP certified?
GAO found no published average duration, and FedRAMP does not promise one. What FedRAMP does publish is a target for its own half of the clock. Among its FY27 goals, FedRAMP commits to keeping initial assessment decisions within 30 days of application.
However, that target applies to the review, not to your engineering work. Plan your own timeline around the evidence you can automate today. Also note a separate limit from GAO: temporary FedRAMP authorizations run for a maximum of 12 months.
Every FedRAMP certification deadline for 2026 and 2027
So this is the table to keep. Every date comes from FedRAMP’s own published timeline.
| Date | What happens |
|---|---|
| July 4, 2026 | Optional early adoption of the Consolidated Rules for 2026 begins |
| July 6, 2026 | Initial Implementation Marketplace listings open |
| July 28, 2026 | FedRAMP Ready goes legacy and stops accepting submissions |
| August 3, 2026 | FedRAMP 20x Class A pipeline opens |
| August 10, 2026 | Temporary Rev5 pipelines open for Class B and C (Ready Conversion, Lost Sponsor) |
| August 31, 2026 | FedRAMP 20x Class B and C pipelines open |
| January 1, 2027 | Consolidated Rules take mandatory effect for all stakeholders |
| February 1, 2028 | All grace periods for the Consolidated Rules for 2026 expire |
| June 11, 2027 | FedRAMP stops accepting applications for new Rev5 certifications |
Above all, two of these have teeth. January 1, 2027 is when certified providers must follow the 2026 rules to keep certification. June 11, 2027 closes the Rev5 door for good. One caveat on the January date: it is not a clean single switch. Area-specific dates apply, and all grace periods run until February 1, 2028. New 20x applications have had to follow the rules since July 4, 2026.
The Ready Conversion and Lost Sponsor pipelines deserve a note, because they are small and they close soon. FedRAMP reported 40 applications to that pathway, with 17 listed as Lost Sponsor and 23 as Ready Conversion. However, the program does not state that every application became a certification. FedRAMP does not plan to widen eligibility before the Rev5 sunset.
Is FedRAMP certification worth it? What the spending data says
Here is the part most FedRAMP guides skip. They explain the process and never tell you the size of the prize.
In FY2025, federal agencies obligated $3.38 billion on contracts coded to NAICS 518210, the code for computing infrastructure, data processing, and web hosting, per USASpending.gov. Small businesses won $1.37 billion of that, or 40.5%. Software publishers (NAICS 513210) added $1.73 billion, with $497.5 million going to small businesses.
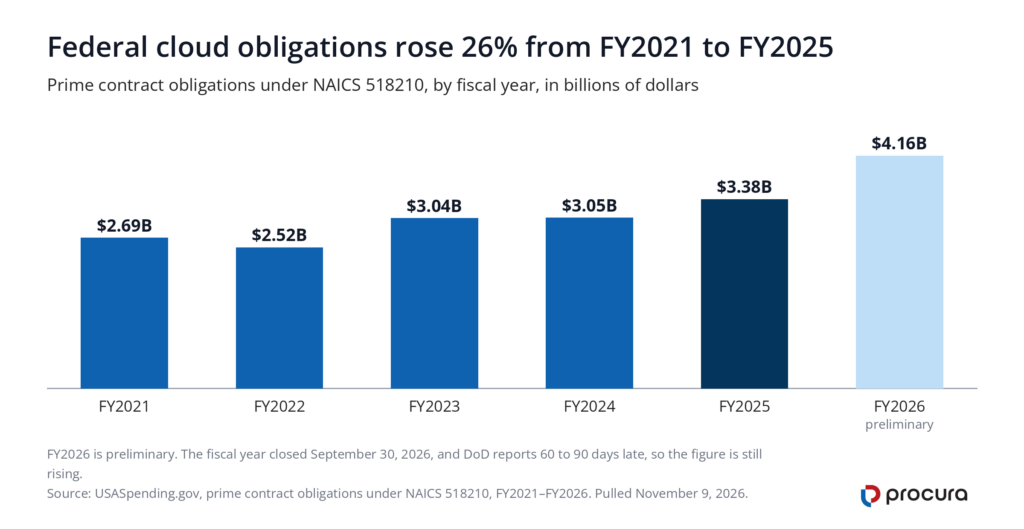
Also, for wider context, GAO reported in June 2026 on a decade of growth. Federal cloud contract spending grew from $2.3 billion to over $10 billion a year. GAO counts cloud more broadly than a single NAICS code does, so treat the two figures as different measurements rather than a contradiction.
| Fiscal year | NAICS 518210 obligations |
|---|---|
| FY2021 | $2.69 billion |
| FY2022 | $2.52 billion |
| FY2023 | $3.04 billion |
| FY2024 | $3.05 billion |
| FY2025 | $3.38 billion |
| FY2026 | $4.16 billion (preliminary) |
Do small businesses need a set-aside to win cloud contracts?
Now the finding that changes how you read the 40.5%. Small businesses won $1.37 billion in NAICS 518210 in FY2025. Only $226.2 million of that came from small business set-asides. The remaining $1.14 billion, about 83%, was won in open competition.
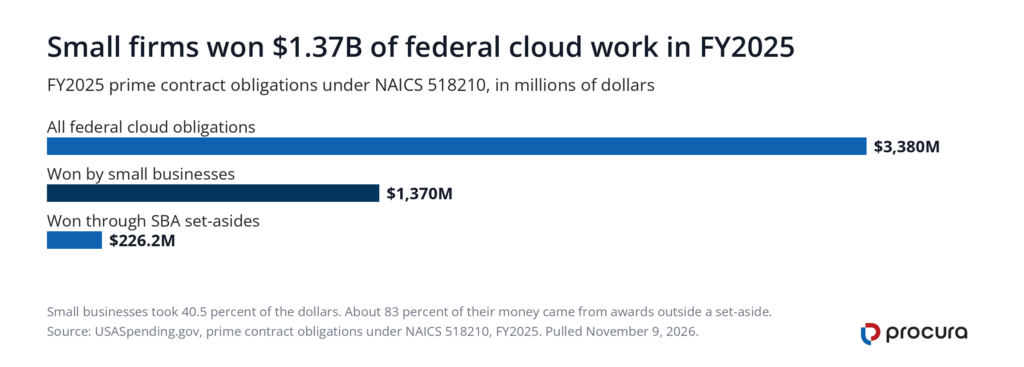
Indeed, that number says something specific about this market. In most federal verticals, a small business wins on set-aside status. In cloud, it wins on the product. Your socioeconomic certifications matter less here than in construction or services work. Your FedRAMP certification matters more, because certification is the gate agencies check.
Small businesses also take a 40.5% share of cloud dollars against roughly 28% government-wide. The federal cloud market is friendlier to small vendors than the federal market as a whole.
Which agencies buy the most cloud?
So target your capture work with this. Defense dominates, but the civilian agencies below it are reachable for a small vendor.
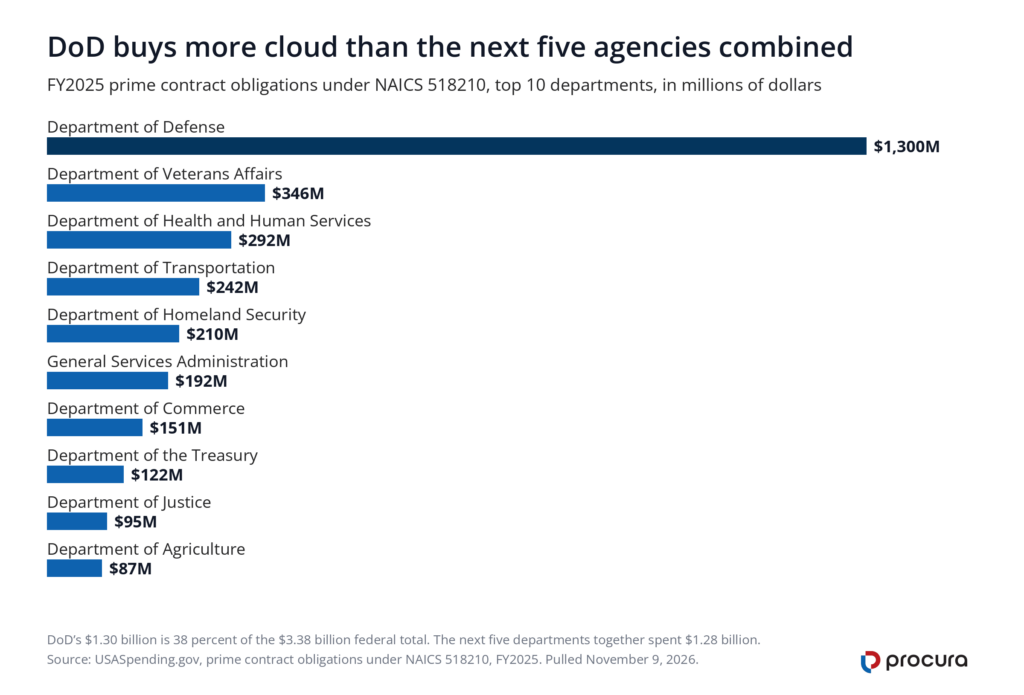
| Rank | Agency | FY2025 obligations (NAICS 518210) |
|---|---|---|
| 1 | Department of Defense | $1.30 billion |
| 2 | Department of Veterans Affairs | $345.9 million |
| 3 | Department of Health and Human Services | $292.4 million |
| 4 | Department of Transportation | $241.6 million |
| 5 | Department of Homeland Security | $209.6 million |
| 6 | General Services Administration | $191.9 million |
| 7 | Department of Commerce | $151.2 million |
| 8 | Department of the Treasury | $121.5 million |
| 9 | Department of Justice | $94.9 million |
| 10 | Department of Agriculture | $87.3 million |
The cloud buyer table above is a snapshot of one fiscal year. The underlying award records stay open to browse at no cost, and you can re-cut them by agency as new obligations post. Create a free account to export a buyer table to a spreadsheet and track it yourself.
How crowded is the FedRAMP Marketplace?
Less crowded than the spending suggests. FedRAMP closed FY2026 with 538 certified cloud service offerings in total. It granted 92 new certifications that year, 66 through Rev5 and 26 through 20x, plus 71 listings in the new Initial Implementation category. Agencies issued 760 new authorizations against those services.
Then put those numbers together. A few billion dollars a year of federal cloud buying passes through a catalog of about five hundred services. That is a narrow gate, and it is the reason certification is worth the cost when you clear the government-wide use test.
However, the 20x queue is busier than the certification count shows. FedRAMP reported on November 2, 2026 that nearly 100 companies have started the FedRAMP 20x process, and that 26 companies hold limited pilot certifications. FedRAMP granted the first 20x Class A certification on August 25, 2026. It granted the first Class C certification that met the full Consolidated Rules for 2026 on October 29, 2026. The program took over 17 months from the 20x announcement to that first Class A award.
That is the useful read on timing. The rules are new enough that very few vendors have finished a full 20x certification, and crowded enough that waiting has a cost.
Even so, one caution on timing. FedRAMP ended FY2026 with 17 federal employees and 15 contractors. That is more than 50% below its staffing of two years earlier. The program spent a little under $9 million of a $10 million budget. A program running lean is a program where your package quality decides your queue time.
What happens to existing Rev5 certifications?
Rev5 is not dead yet, but it closes on a published schedule. New Rev5 applications stop on June 11, 2027. Existing Rev5 certifications must adopt the Consolidated Rules for 2026 from January 1, 2027. Initial Rev5 certification under the new rules starts January 1, 2027. Ongoing certification for the two types starts the same day.
Meanwhile, FedRAMP expects to publish transition paths and timelines for moving legacy Rev5 services to 20x by the end of FY27. If you hold a Rev5 certification today, your work for the next year is to adopt the 2026 rules, not to switch types.
In short, for most vendors starting now, the calculation is simple. A new 20x certification carries you past the two deadlines. A new Rev5 certification buys you a path that FedRAMP has already scheduled for retirement.
After you are certified, you still have to find the work
Certification gets you into the catalog. It does not tell you which agency buys, which solicitation suits you, or which requirement buried in an attachment disqualifies you. That is a separate problem, and it is the one that burns BD time.
The federal market publishes its intentions in plain sight. Agencies post requirements, and the requirements that matter usually sit inside attachments rather than the notice itself. Reading them is the work. Most teams do it with a trained person and a lot of hours, the same way they handle proposal responses and SAM.gov registration.
Procura Federal reads every solicitation attachment, scores how well each one suits your capability statement, and flags compliance requirements before you commit a bid team. It costs $399/month. Against the $300,000 floor GAO recorded for FedRAMP authorization, the tool that tells you whether the resulting contracts exist is not the expensive line item.
Do you sell cloud software and want the rest of the picture? Start with our guide to selling software to the government. If you handle controlled unclassified information, read the CMMC Level 1 requirements. If you want a contract vehicle behind the certification, read the GSA Schedule path. The FAR overhaul matters here too. GAO found that the FAR still has no definition of cloud computing, and an IT definition that is 20 years old.
Book a demo. I will show that your certified service has real work to bid on this quarter.